
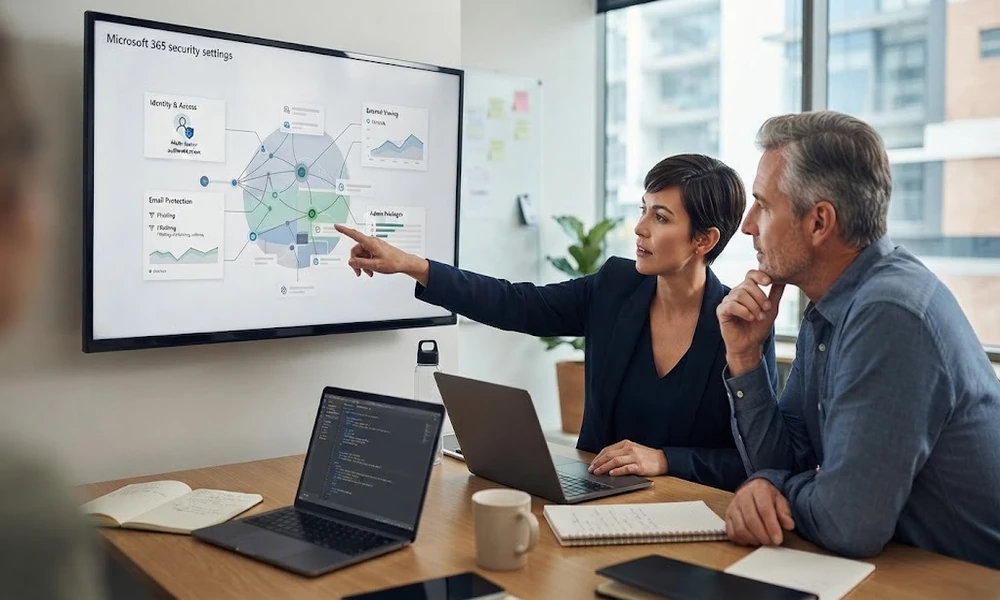
Microsoft 365 is where most growing businesses keep their email, documents, calendars, and team conversations. That concentration makes it extremely useful, and it also makes it one of the most attractive targets for attackers. A single compromised account can expose years of correspondence, shared files, and client data.
The platform includes strong security tools, but many of them are not switched on or tuned by default. Businesses that review their configuration deliberately tend to close the gaps attackers rely on, often without buying anything new.
Why Microsoft 365 Is Such a Common Target
Attackers go where the data is. A typical Microsoft 365 tenant holds sensitive email threads, contracts, financial documents, and login access to other connected applications. Gaining control of one mailbox can also give an attacker a trusted position from which to send convincing messages to clients and colleagues.
Most intrusions do not involve breaking the platform itself. They involve stealing or guessing a user’s credentials, then using normal features to read mail, forward messages, or share files. This is why identity and access settings deserve the first look in any review.
Multi-Factor Authentication and Conditional Access
Multi-factor authentication remains the single most effective control against stolen passwords. A review should confirm that it is enforced for every user, including administrators and shared or service accounts that are easy to overlook, rather than merely available as an option.
Conditional access policies add context to each sign-in. They can require extra verification for unfamiliar locations or unmanaged devices, and block sign-ins that use outdated authentication methods which bypass modern protections. These rules let a business stay convenient for legitimate users while making life much harder for someone using a stolen password.
Email Protection and Suspicious Mailbox Rules
Email is the most common way attackers reach employees, so protection against phishing, malicious attachments, and impersonation should be configured and tested. This includes filtering for look-alike sender names and domains, which are often used to mimic executives or vendors.
One of the quieter signs of a compromised mailbox is a hidden forwarding rule that silently copies incoming mail to an outside address. Reviewing for unexpected rules, and restricting automatic external forwarding where it is not needed, helps catch an intrusion that would otherwise go unnoticed for weeks.
Sharing Settings in SharePoint, OneDrive, and Teams
Collaboration tools make it easy to share files, and that convenience can quietly expand who has access. Settings that allow anyone with a link to open a document, or that let users invite external guests without review, can leave sensitive files exposed long after a project ends.
A sensible review sets clear defaults for external sharing, limits anonymous links for sensitive libraries, and checks which external guests still have access. It also looks at who owns each Team and site, since abandoned spaces with no owner tend to collect stale permissions.
Administrator Accounts and Least Privilege
Administrator accounts hold the keys to the entire environment, so they need tighter control than ordinary accounts. Best practice is to keep the number of administrators small, give each person only the role they need, and use separate accounts for administrative work rather than everyday email and browsing.
Regularly reviewing who holds privileged roles also catches the common problem of former employees or contractors who still have elevated access. Fewer, well-protected administrator accounts reduce both the chance of compromise and the damage if one occurs.
Logging, Alerts, and Backup
Security settings are far more useful when someone is watching them. Audit logging, sign-in monitoring, and alerts for unusual activity such as impossible travel, mass file downloads, or new inbox rules give a business the chance to respond quickly rather than discover a problem after the damage is done.
Backup deserves a separate mention. Microsoft 365 provides availability and some recovery features, but it is not a full backup of a business’s data. Accidental deletion, malicious deletion, and ransomware can all result in lost content, so many businesses add independent backup for mailboxes, files, and Teams data.
How Mindcore Technologies Helps Businesses Secure Microsoft 365
Mindcore Technologies has spent more than 30 years helping businesses build secure, reliable technology environments, and as a Microsoft Partner, supports organizations in configuring and managing Microsoft 365 properly. Under the leadership of Matt Rosenthal, CEO of Mindcore Technologies, the company delivers IT solutions in Miami that include Microsoft 365 management, multi-factor authentication rollouts, 24/7 monitoring, and endpoint protection.
Businesses working with Mindcore get a Microsoft 365 environment reviewed against real attack patterns, with the settings tuned and monitored on an ongoing basis rather than left at their defaults.
Conclusion
Microsoft 365 gives growing businesses powerful tools, but its security depends heavily on how it is configured. Enforcing multi-factor authentication, tightening email protection and sharing settings, limiting administrator access, monitoring for unusual activity, and adding independent backup addresses most of the weaknesses attackers exploit. A periodic review of these settings is one of the most practical and cost-effective security steps a business can take.
About the Author
Matt Rosenthal is the CEO and President of Mindcore Technologies, a full-service IT consulting and cybersecurity firm serving businesses across Florida, New Jersey, Maryland, South Carolina, Louisiana, Texas, and nationwide.
With more than 30 years of experience in IT leadership, managed services, and technology strategy, Matt has helped organizations across healthcare, financial services, and professional services secure their collaboration and cloud environments. He holds an MBA in Technology Management, is a certified Project Management Professional (PMP), and is the host of Digging In, a weekly podcast on success in business, life, and health.